Compliance and Regulation
Compliance and Regulation
How compliance programmes, anti-money-laundering checks, monitorships and digital evidence work inside companies and regulated firms.
Compliance is the part of a company that has to know the rules and prove that it followed them. It is not the same as legal advice and it is not only paperwork. A compliance programme is a set of controls that a firm designs, runs and tests, so that it can show a regulator, a bank, an insurer or a court that it took its obligations seriously before anything went wrong.
Why compliance became a board subject
Three forces pushed compliance from a back office to the boardroom. The first is anti-money-laundering law, which made financial and other regulated firms responsible for knowing who their customers are. The second is anti-corruption law, which made companies liable for the acts of people acting for them, including intermediaries and agents. The third is the growth of digital evidence, which means that a firm's own systems now hold a detailed record of what it did and when. Together they changed the question from whether a firm meant well to whether it can show, in documents and data, what it actually did.
The elements of a programme that a regulator expects
Most frameworks describe a similar set of elements. A written policy that senior management has approved. A person or function with real authority and resources to run it. A risk assessment that is specific to the firm rather than copied from a template. Training that reaches the people who face the risk. A way for staff to report concerns without fear. Monitoring and testing that finds weaknesses before an examiner does. And a record of all of it, because an untested programme and an undocumented programme look the same from outside.
The guide to KYC and AML takes the part of this that applies to every customer relationship: identity, ownership, source of funds and the monitoring that continues after onboarding.
Knowing the customer, and knowing the owner behind the customer
Know-your-customer rules began as a way to confirm that a person is who they claim to be. They now reach further. A firm is expected to understand the nature of a customer's business, to identify the people who ultimately own or control it, and to judge whether the relationship makes sense. That last step is where most failures occur. A company can pass an identity check and still be an implausible customer: a shell with no staff, an address shared with hundreds of others, or a business that has no visible reason to move the sums it moves.
Anti-money-laundering law adds a duty to monitor. Onboarding is a moment, but a relationship is a duration. A customer who was unremarkable when accepted can become a concern later, and the rules expect the firm to notice. The practical consequence is that compliance is never finished; it is a cycle of assessment, monitoring and review.
When a firm is placed under a monitor
Some compliance failures are resolved by agreement rather than prosecution. In those settlements, a firm may accept an independent monitor whose job is to test whether the promised reforms are real. A monitorship is unusual because it puts an outsider inside the firm with a mandate to report to someone else, often a regulator or a prosecutor. The guide to compliance monitoring and monitorships explains what a monitor tests, who receives the reports, and how the arrangement is brought to an end.
Digital evidence, which is now most evidence
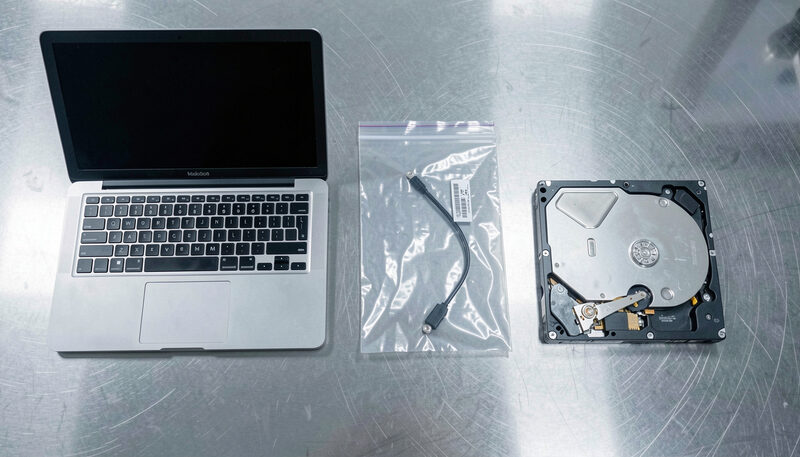
Almost every modern compliance question is answered by data. Email, chat, transaction logs, access records, mobile devices and cloud accounts hold the facts of what happened. That makes the handling of digital evidence a compliance subject in its own right. A firm that cannot preserve a device without altering it, or cannot show who had access to a log, may lose the ability to prove a case it would otherwise win. The guide to cyber crime and digital evidence sets out how devices and logs are identified, preserved without change and handed over with a chain of custody a court will accept.
The cost of a programme that exists only on paper
The most expensive compliance failures are rarely the absence of a policy. They are policies that no one followed, training that no one attended, alerts that were closed without being looked at, and a culture in which raising a concern was risky. Regulators have learned to test for this by asking not what the rules say but what happened in a specific case, and by comparing the answer with the firm's own records. That is why the discipline of investigation, described in the section on fraud and corporate investigations, is inseparable from compliance: a firm that cannot investigate its own failures cannot fix them.
The guides in this section
The section covers KYC and AML, compliance monitoring and monitorships, and cyber crime and digital evidence.
Compliance and Regulation
Cyber Crime and Digital Evidence
How digital evidence is handled in a cyber crime case: identifying devices and logs, preserving them without change, and the chain of custody a court expects.
Devices, logs and the chain of custody a court expects.
Compliance and Regulation
Compliance Monitoring and Monitorships
How a compliance monitor or monitorship works after a settlement: what the monitor tests, who it reports to, and how the arrangement ends.
What a monitor tests, who it reports to, how it ends.
Compliance and Regulation
KYC and AML: What Due Diligence Asks
What know-your-customer and anti-money-laundering checks require of a firm, from identity and ownership to source of funds and ongoing monitoring.
Identity, beneficial ownership, source of funds and monitoring.